Consumers reported losing $15.9 billion to fraud in 2025, up from over $12 billion in 2024, according to the Federal Trade Commission (FTC). Many fraud programs stall at upkeep: rules go stale, feedback never reaches the model and small teams run out of time to tune them.
Fraud risk management is the ongoing process of identifying, assessing and controlling the fraud risks a business faces, then measuring and refining those controls as attacks change.
This guide walks through a five-step framework and helps you decide who should run it.
quick summary
Understanding Fraud Risk Management
Fraud risk management covers every threat a business faces, from external attacks such as account takeover, payment fraud, synthetic identities and promo abuse to internal fraud by employees or partners. Detection is one control inside that wider program, alongside governance, measurement and continuous improvement.
It is a continuous loop rather than a one-time compliance exercise, because the risks themselves keep changing. Our vendor comparison for fraud management systems covers the tools that run these controls.
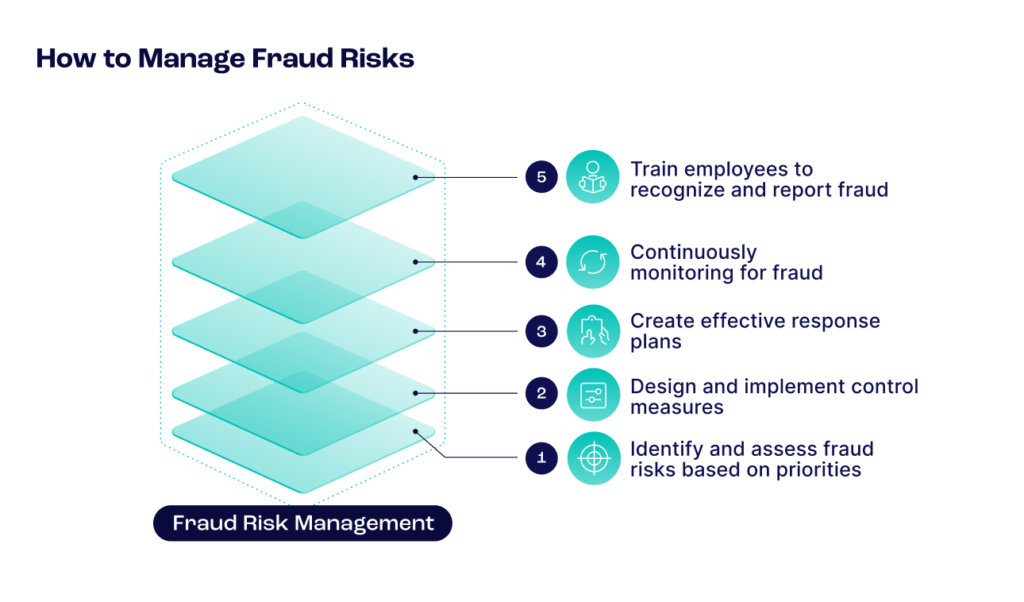
The 5 Steps of a Fraud Risk Management Framework
Each step feeds the next and the last step sends you back to the first. Use them as a repeatable process, not a checklist you complete once.
1. Assess Your Fraud Risks
Start by mapping every point where fraud can hit your business: sign-up, login, payment, withdrawal and account changes such as a new phone number or payout method. For each touchpoint, list the fraud types that apply, then rate their likelihood and impact using your own loss and chargeback data.
| Fraud risk | Where it hits | Likelihood | Impact | Priority |
| Fake account creation | Sign-up | High | Medium | High |
| Account takeover | Login, account changes | Medium | High | High |
| First-party fraud | Application, payment | Medium | High | High |
| Card testing | Payment | Medium | Medium | Medium |
| Promo or bonus abuse | Sign-up, first deposit | High | Low | Medium |
Fraud risk assessment checklist
- Map every customer touchpoint where money or personal data moves
- List the fraud types that apply at each touchpoint
- Rate likelihood and impact using your own fraud, loss and chargeback data
- Note the controls regulators expect you to show, even if they catch little fraud
- Set your risk appetite: how many legitimate customers you will challenge to stop one fraudster
- Repeat the assessment whenever you launch a new product or enter a new market
Watch for overlapping risks. In lending, a genuine applicant can still be too high a credit risk, so agree which team owns the fraud decision and which owns the credit decision before you write rules for either.
2. Assign Ownership and Governance
Name a single owner for fraud strategy and separate the people who set strategy from the people who implement rules. Fraud and anti-money laundering (AML) often split here: compliance owns AML strategy, while risk or product teams run the day-to-day rules.
Then set a change process. When several product teams share one ruleset, a rule changed for one product can break another. A simple escalation matrix that defines who can request a change, through which channel and who approves it prevents those unintended consequences.
Finally, report fraud losses and risk posture to senior leadership on a fixed schedule. Regular visibility keeps budget and headcount aligned with the risk the business actually carries.
3. Deploy Prevention and Detection Controls
Layer controls across the customer journey instead of relying on a single checkpoint. Each layer catches a different kind of fraud and together they let you approve good users quickly while stopping bad ones early.
- Digital footprint checks: confirm an email and phone number have real online history at sign-up, before you run costlier identity verification
- Device intelligence: flag emulators, device farms and multiple accounts created from the same environment
- Behavioral and session monitoring: catch bots, remote access and coached users during sensitive actions such as payments or payout changes
- Transaction monitoring and velocity rules: spot card testing, mule activity and unusual money movement as it happens
Set approve, review and decline thresholds that reflect your risk appetite and treat them as low, medium and high risk. Keep score bands configurable so you add a manual review state only where the cost of an analyst is justified. Learn more about running these checks in real-time fraud detection.
4. Measure and Report Performance
You cannot manage fraud risk you do not measure. Track a short set of key performance indicators (KPIs) every month and review them alongside your risk assessment.
| KPI | What it tells you |
| Fraud rate | Whether your controls are stopping fraud, measured as confirmed fraud or losses as a share of volume |
| False positive rate | How many legitimate customers your rules block or challenge |
| Decline rate | Whether tightening rules is starting to hurt conversion |
| Manual review rate and time | How much analyst workload and cost your thresholds create |
| Chargeback rate | How much payment fraud slipped through |
| Rule trigger rate | Which rules still earn their place in your ruleset |
Label outcomes on both sides. Many teams mark confirmed fraud but never mark customers they declined by mistake, so their models learn only half the picture. Feed back chargebacks, confirmed fraud and false positives. Then hold out a small control group to measure what your rules are really declining.
5. Review and Refine Continuously
Fraud controls decay over time, because fraudsters adapt, products change and data fields get renamed. In one SEON audit of a lending customer, dozens of active rules had not fired all year and an integration change had silently broken exclusions across several rule groups.
- Audit your rules: retire rules that no longer trigger and re-weight rules that over-penalize good users
- Test before you deploy: backtest changes on historical data or run them in shadow mode with zero weight
- Recheck after every change: confirm rules still fire as expected after any integration, product or data update
- Set a review rhythm: review fraud trends weekly and run a deeper performance audit monthly or quarterly
Who Should Run Your Fraud Risk Program?
Every step above needs regular attention, from reviewing alerts to tuning thresholds and updating block and allow lists. Large enterprises staff dedicated fraud teams, but many businesses run fraud with a handful of people who also own product, payments or compliance.
That gap is where programs stall. Teams write rules at launch and never revisit them, manual reviews back up and nobody has time to label outcomes. The work still has to happen, so the real decision is who does it.
| In-house fraud team | Managed fraud services | |
| Best for | Established fraud functions with dedicated analysts | Small or new teams, product launches and new markets |
| Time to expertise | Months to hire, train and ramp up | Immediate access to experienced fraud investigators |
| Cost | Salaries, hiring and training | Ongoing service fee |
| Control | Full control of strategy and rules | Shared, with ownership agreed up front |
| Continuity | Knowledge can leave when analysts do | Documented playbooks and handovers |
Many teams combine both. Consultants set up and tune rules during a launch, then hand over to an in-house hire, or they stay on to run weekly reviews while the internal team owns strategy.
Consider managed fraud services if your team has:
- No dedicated fraud analyst
- A new product or market launch coming up
- A growing manual review backlog
- Rules that have not been reviewed in months
- False positives it cannot trace to specific rules
How SEON Supports Fraud Risk Management
Most teams need reliable controls and the people to run them — SEON provides both. Digital footprint and device intelligence check sign-ups, logins and transactions in real time, while explainable rules and artificial intelligence (AI) scoring show which signals drove each decision. Teams can also backtest changes before they go live.
For teams that need extra expertise, SEON’s Managed Risk Services adds a dedicated senior fraud consultant who reviews suspicious activity daily, optimizes rules and risk scoring, runs weekly trend analysis and delivers monthly fraud posture audits. In one Hidden Risk Files investigation, SEON fraud consultant Kyle Truax linked nearly 200 accounts on a rewards platform that shared no device ID at all.
“The identifiers were disposable by design. The deeper device signals underneath them weren’t.”
Kyle Truax, Fraud Consultant
Adapting to Regulatory Change
Regulators are extending AML obligations beyond traditional financial institutions, so more sectors now need documented controls and evidence that they work.
Real-time payments add pressure, because fraudsters exploit instant transfers to move and launder money before anyone reviews them. Monitoring transactions as they happen, with AML transaction monitoring and case management in the same workflow, keeps your program aligned with current and upcoming rules.
See our best practices for transaction monitoring in AML.
Frequently Asked Questions:
What is fraud risk management?
Fraud risk management is the ongoing process of identifying, assessing and controlling an organization’s fraud risks, then measuring and refining those controls as threats change. It combines governance, prevention and detection tools, performance tracking and regular reviews.
What are the five steps of fraud risk management?
Assess your fraud risks, assign ownership and governance, deploy prevention and detection controls, measure and report performance, then review and refine your controls continuously. The final step feeds back into a fresh risk assessment.
What are the components of an effective fraud risk management program?
A current risk assessment, a clear owner and change process, layered controls across the customer journey, a small set of KPIs, labeled outcomes for both fraud and false positives and a fixed schedule for reviewing rules.
How often should you review fraud rules?
Review fraud trends weekly and audit rule performance at least monthly or quarterly. Also recheck rules after any integration, product or data change, since a renamed field can silently stop a rule from firing.